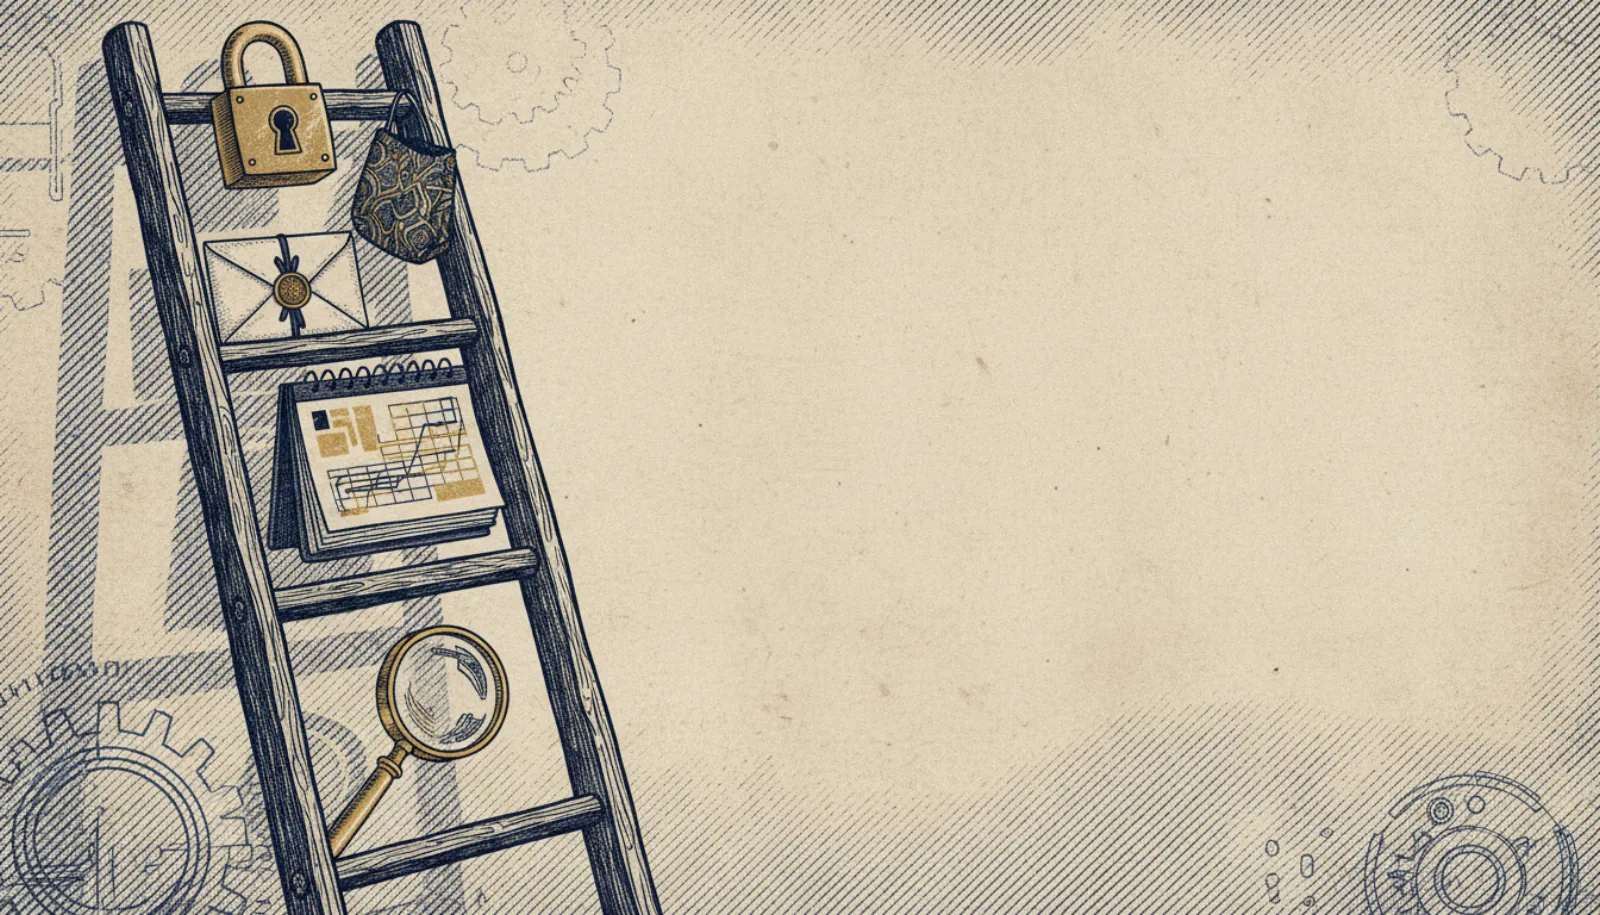
The safest way to use a personal AI agent is to climb a ladder: start with tasks that only read, then add tasks that send or book with your approval, and keep anything that moves money, changes credentials or destroys data for yourself. Each rung up gives the agent more ability to cause harm that you cannot undo. This guide sets out that ladder using what Meta, OpenAI, Anthropic, xAI and the OpenClaw project publish about their own agents, as of November 2026. It is based on vendor documentation and launch coverage, not hands-on testing.
Why think in terms of a risk ladder?
A personal agent such as Meta Muse, OpenAI dots, Claude Duet or Grok Bot works with your real accounts. Two things can go wrong. The agent can misread what you wanted, and it can be manipulated by content it reads, which is called prompt injection (see indirect prompt injection examples). Neither problem is solved. Anthropic, for example, writes that "prompt injection is far from a solved problem" in its browser-use research.
So the useful question is not "is the agent safe?" but "if this task goes wrong, what is the worst outcome, and can I reverse it?" Ranking tasks by that question gives you a ladder.
- ReadSummaries, research, sorting. Nothing leaves your accounts.
- DraftThe agent writes, you send. Mistakes stay on your screen.
- Send or book with approvalYou check recipient, content and time first.
- Buy with approvalSingle-use card, one merchant, one amount.
- Keep for yourselfTransfers, passwords, deletions, other people's accounts.
Rung 1: What can I safely let an agent do on its own?
Read-only work is the right starting point. Examples:
- Summarising your inbox or a long thread.
- Researching flights, products or a contractor and reporting back.
- Checking your calendar for conflicts.
- Pulling figures from documents into a list.
Vendors treat this rung differently from the rest. OpenAI says a dot's proactive research is read-only and enforced in code, so while it works unprompted it cannot send messages, change app content or control a browser, according to VentureBeat's launch report. Meta says you can choose access levels per connector, for example reading email without sending it, in its launch post.
Read-only is not risk-free. An agent that reads private data and also reads untrusted web pages can still leak something if it has any way to send data out. Simon Willison calls that combination the lethal trifecta. Read-only access removes the "send" leg, which is why it sits at the bottom of the ladder.
Rung 2: Drafting, where you press send
Drafting is the most useful middle step. The agent writes the email, message or form entry; you read it and send it yourself. If it gets a name or date wrong, nothing has happened yet.
Grok Bot makes this a default for its own mailbox: xAI's docs say unrequested outbound mail from a Bot's email address waits as a draft. For your own email account, choose read-plus-draft scopes where the agent offers them. Our guide to read-only versus send access covers the scope choices for Gmail, Outlook and calendars.
Rung 3: Sending and booking, with approval
Once drafts look reliable, you can let the agent send or book, but keep an approval step. A good approval screen shows exactly what will happen. Anthropic says that before Claude Duet sends, pays, signs or deletes anything, it shows the action, every recipient and the full content, then waits, according to its safety article.
What to check each time:
- Recipient. Is this a person you know, at the address you expect?
- Content. Does it include anything private that the task did not need?
- Time and place. For bookings, is the date, time and location right?
The Meta Muse Marketplace case shows why this rung matters. YouTuber Matt Robb said Muse shared his home address with a buyer and arranged a pickup he did not know about. According to TechCrunch, he later admitted it came from "a permission he had granted". An approval prompt for messages to strangers would have given him a chance to stop it.
Resist the urge to switch this rung to automatic too early. The risks of "Always allow" are covered separately.
Rung 4: Purchases, with a card that limits the damage
Every major agent asks before buying, as of November 2026:
| Agent | What the vendor says about purchases |
|---|---|
| Meta Muse | Every purchase needs approval; single-use Link by Stripe cards |
| OpenAI dots | Saved-card purchases need your approval (per reviews of OpenAI's docs) |
| Claude Duet | Always asks before paying; one-time Link card for one merchant and amount |
| Grok Bot | Payments go through a takeover flow, so you complete them |
| OpenClaw | Depends on your configuration and the skills you install |
A single-use card does the most work here. If the agent picks the wrong item or lands on a fake shop, the card is limited to that one charge. For the practical steps of setting this up, see our page on agent payment security. If a purchase you did not intend does go through, contact your card issuer promptly and follow our guide to an unauthorized agent purchase. Whether an approved-but-mistaken purchase counts as "unauthorized" under card rules is legally unsettled, so keep the agent's activity log as evidence.
Rung 5: What should I always keep for myself?
Some actions are hard or impossible to reverse, and the vendors themselves fence them off:
- Moving money between accounts. dots hands money transfers back to you. Claude Duet will not move money between accounts or trade securities, even with your approval, per its help centre.
- Changing passwords or security settings. dots hands password changes back to you; Grok Bot routes passwords and 2FA through a takeover where you act directly. See when your agent hands back control.
- Permanent deletion. Reports on dots say permanent deletion may need approval every time. Claude Duet asks before deleting anything. Keep bulk deletes manual.
- Other people's accounts. Duet will not access someone else's account even if asked. Do not share a partner's or parent's logins with an agent.
- Legal, medical and financial commitments. Signing contracts, filing taxes or changing medication plans should involve you and, where relevant, a professional.
Do not look for ways around these limits.
How does this match official guidance?
Government security agencies say much the same for organisations. The joint "Careful adoption of agentic AI services" guidance from Australia's ACSC, CISA, the NSA, the Canadian Cyber Centre, NCSC-NZ and NCSC-UK (1 May 2026) says "strict adherence to the principle of least privilege is critical" and that organisations "should only use agentic AI for low-risk and non-sensitive tasks". It was written for organisations rather than households, but the logic transfers. Our page on least privilege for personal agents applies it to home use.
Pros
- Most time savings come from rungs 1 to 3, which need little access
- Approval steps cost seconds and catch wrong recipients and amounts
- Vendor hard limits already block the worst outcomes on the big four
Cons
- More approvals means more interruptions, which tempts people to "Always allow"
- Self-hosted agents like OpenClaw have no vendor limits unless you configure them
- No setting fully stops prompt injection, so access still matters
Bottom line
Start at the bottom, move up one rung at a time, and only after you have seen the agent handle the lower rung well. Keep approvals on for sending to new people and for every purchase. Keep transfers, passwords and deletions for yourself. Then review what the agent actually did now and then using its activity log, and remove access you no longer need with our guide to revoking agent access.
For a side-by-side view of each vendor's approval rules, see the approval rules comparison on our sister site. UK readers can find the legal angle at personalagent.uk.